The True Price of Keeping Everything: How Data Hoarding Quietly Drains Your Compliance Budget
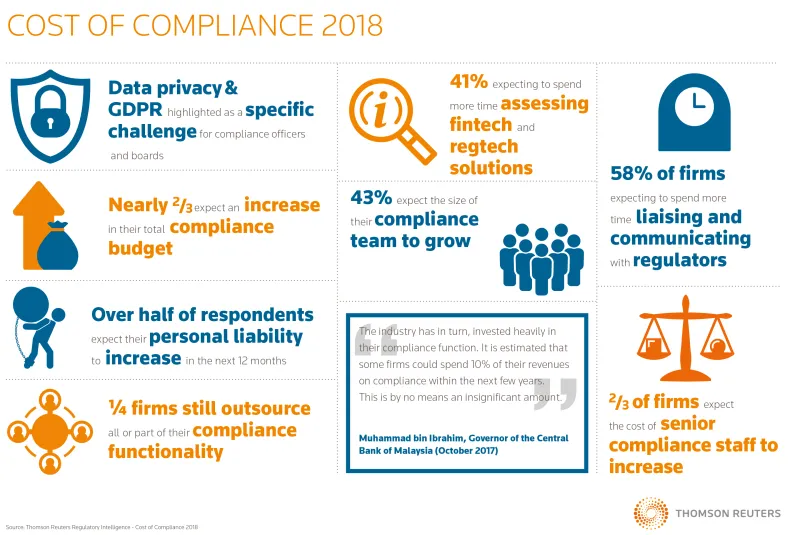
Photo: enterprise compliance cost analysis data management office, via legal.thomsonreuters.com
For years, the prevailing logic in enterprise data management followed a simple principle: storage is cheap, so keep everything. Hard drives got less expensive. Cloud infrastructure scaled on demand. The friction of discarding data seemed to outweigh any conceivable benefit. What that calculus consistently failed to account for, however, was the compounding regulatory and operational liability that accumulates alongside every terabyte retained past its useful life.
The result is a quiet but significant drain on enterprise compliance budgets—one that most organizations never fully attribute to their data strategy.
The Invisible Balance Sheet of Excess Retention
When finance teams calculate the cost of a data breach or a regulatory penalty, they rarely trace the root cause back to retention policy. Yet the connection is direct. The more data an organization holds—particularly sensitive, personally identifiable, or regulated data—the larger the attack surface, the greater the disclosure scope in any incident, and the heavier the potential penalty under frameworks like HIPAA, CCPA, and the FTC's evolving data security standards.
Consider the math. Under CCPA, California's Consumer Privacy Act, violations can reach $7,500 per intentional infringement. For an enterprise that has accumulated millions of consumer records it no longer needs for any legitimate business purpose, a single enforcement action can translate into exposure that dwarfs years of storage savings. That is before accounting for legal fees, remediation costs, and the operational disruption of a regulatory inquiry.
A 2023 analysis by the Ponemon Institute found that organizations with mature data minimization practices experienced breach costs approximately 18 percent lower than those with undisciplined retention policies. The mechanism is straightforward: less data means fewer records to breach, fewer notifications to issue, and a narrower scope for any subsequent investigation.
Case Study: A Regional Healthcare Network Recalibrates Its Approach
A mid-sized regional hospital network operating across four states faced a compliance audit following a third-party vendor incident. The network had retained patient records well beyond the federally required retention windows—not out of clinical necessity, but because no formal deletion protocol had ever been established. When investigators assessed the breach scope, the volume of out-of-retention records significantly expanded both the notification obligations and the potential HIPAA penalty calculation.
Following the incident, the network engaged a data governance consultancy to implement a structured data lifecycle program. Over eighteen months, the organization purged approximately 40 percent of its stored patient data—records that carried regulatory exposure but zero operational value. The outcomes were measurable: annual storage costs dropped by $1.2 million, incident response simulation exercises ran faster and at lower cost, and the organization's cyber liability insurance premium decreased at renewal, as the insurer recognized the reduced risk profile.
The network's Chief Compliance Officer noted that the most significant shift was cultural. Teams that had previously resisted deletion out of vague concern about future utility began to understand retention as a liability decision, not merely an infrastructure one.
Incident Response Costs: The Multiplier Effect
Beyond regulatory penalties, excess data retention inflates the cost of incident response in ways that are rarely modeled in advance. When a breach occurs, forensic investigators must assess the full scope of compromised data. Every additional database, archive, or legacy system containing sensitive information extends the investigation timeline, increases vendor fees, and delays the organization's ability to issue required notifications.
Under most US state breach notification laws, notification timelines are tight—typically between 30 and 72 hours for certain regulated industries. Organizations carrying large volumes of unstructured or poorly catalogued legacy data frequently struggle to meet these windows, not because of technical failure, but because they cannot determine with confidence what data was actually exposed. That uncertainty carries its own cost, often leading to over-notification that generates reputational damage and consumer relations expenses beyond the incident itself.
A financial services firm that implemented a formal data classification and retention program reported that its average incident response cycle time dropped by 34 percent after the program's first full year. The reduction came almost entirely from improved data inventory practices—knowing precisely what data existed, where it lived, and what its classification status was.
The ROI of Deliberate Data Stewardship
The business case for disciplined data governance is not merely defensive. Organizations that establish clear retention schedules, automate deletion workflows, and conduct regular data audits consistently report secondary benefits that extend beyond compliance.
First, leaner data environments are materially easier and less expensive to secure. Security tooling costs—whether for endpoint protection, data loss prevention, or encryption management—scale with data volume and complexity. Reducing the footprint reduces the tooling burden.
Second, audit readiness improves dramatically. When regulators or enterprise customers request evidence of data handling practices, organizations with structured governance programs can respond quickly and with documented precision. That capability has real commercial value, particularly in B2B contexts where procurement teams increasingly scrutinize vendor data practices as part of their due diligence process.
Third, internal operational efficiency gains are measurable. Data teams spend less time managing redundant or obsolete records, analytics pipelines run on cleaner datasets, and discovery requests in litigation become significantly less burdensome.
Building a Retention Framework That Pays for Itself
The practical path forward for most enterprises begins with a data inventory—a candid accounting of what is held, where it resides, why it was collected, and whether a legal or operational basis for continued retention exists. From that foundation, retention schedules can be established by data category, automated deletion workflows can be configured, and exception processes can be documented for data that legitimately warrants extended retention.
The investment in building this infrastructure is real, but it is finite. The cost of not building it compounds indefinitely.
For enterprises serious about treating data governance as a strategic function rather than a compliance checkbox, the starting point is a simple reframe: every record retained without purpose is not a free asset. It is an unpriced liability. When organizations begin accounting for data that way, the economics of stewardship become self-evident—and the hidden costs of hoarding finally appear on the balance sheet where they belong.